Security problems rarely begin with an attacker magically breaking encryption. More often, they begin with an assumption developers never questioned.
Maybe an app assumes a deep link always comes from its own website. Perhaps a backend trusts an account ID supplied by the client.
A WebView loads external content while exposing native functionality, or an exported component accepts data from any installed application.
This is where advanced threat modeling for modern Android applications becomes valuable.
Threat modeling is a structured way to ask what you are protecting, who might attack it, where trust changes, what could go wrong, and which defenses deserve the most attention.
OWASP describes threat modeling as a foundational activity involving the identification, enumeration, prioritization, and early handling of threats during architecture and design.
For Android teams, that means examining more than Kotlin code.
The real system includes the app, operating system, other installed apps, backend APIs, third-party SDKs, storage, network connections, authentication services, and sometimes environments controlled by an attacker.
Start With Assets Instead of Attacks
A useful threat model begins by identifying what actually matters.
If you immediately ask, “How could someone hack this app?” the number of possibilities becomes overwhelming.
Instead, identify valuable assets.
A banking application may care about account balances, session credentials, transfer authorization, personal information, and transaction history.
A streaming platform may care more about subscription entitlements, copyrighted media, authentication tokens, and anti-abuse controls.
Assets can also include less obvious things such as application reputation, availability, privacy, API quotas, and business logic.
Once the assets are clear, security conversations become more focused.
The question changes from:
“What attacks exist?”
to:
“What could happen to this specific asset, and how much would it matter?”
That difference prevents teams from spending weeks protecting low-value functionality while overlooking something critical.
Map the System and Its Trust Boundaries
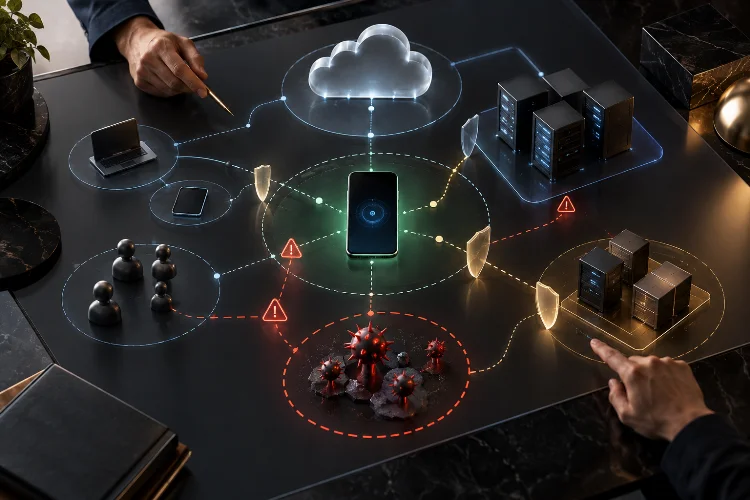
Next, draw how information moves through the application.
You do not need complicated modeling software. Even a simple diagram can reveal important risks.
A modern Android application might look like:
User → Android App → HTTPS API → Backend → Database
But the real architecture may also contain:
Deep Links → App
Other Apps → Exported Components
App → Third-Party SDKs
Web Content → WebView
App → Local Storage
App → Android System Services
Every time data crosses from one security context to another, you have a potential trust boundary.
For example, data coming from your own ViewModel may already have passed several validations. Data arriving from an external Intent has a very different trust level.
Trust boundaries matter because validation rules should usually become stronger when information crosses them.
A system diagram therefore gives developers something extremely valuable: a visual map of where assumptions change.
Identify the Real Android Attack Surface
The attack surface is everything an attacker can potentially interact with.
For Android, this extends far beyond login screens.
Activities, Services, BroadcastReceivers, and ContentProviders may expose entry points. Deep links and App Links can carry attacker-controlled parameters. WebViews may process remote content.
Local files, databases, clipboard operations, notifications, IPC interfaces, and backend APIs can also become part of the attack surface.
Android itself provides strong security defaults, including application sandboxing, secure IPC mechanisms, permission controls, and other platform protections.
The danger often appears when applications intentionally create exceptions.
For example, an exported Service may be necessary for app-to-app communication. That does not make it unsafe by definition.
It does mean the Service should be treated as externally reachable.
Threat modeling turns this into a concrete question:
What happens if a malicious application calls this component with unexpected data?
That question alone can reveal many design flaws before code reaches production.
Define Attacker Capabilities
Not every application faces the same attacker.
A weather app and a digital wallet should not use identical security assumptions.
A basic threat model might assume the attacker can install another malicious app on the same device.
A more sensitive product might assume the attacker controls the device, analyzes the APK, modifies runtime behavior, intercepts application logic, or runs the software in a hostile environment.
OWASP’s mobile testing profiles explicitly distinguish attacker models and recommend selecting controls according to the application’s threat assessment.
This is important because security controls become expensive.
If your threat model assumes a hostile device owner, simple client-side checks are no longer trustworthy.
If you only need protection against ordinary malicious apps, Android sandboxing and platform controls already provide a much stronger starting point.
Write attacker capabilities down clearly.
Otherwise, teams often argue about security controls while secretly working from completely different assumptions.
Use STRIDE as a Thinking Tool, Not a Checklist
STRIDE is a common framework for brainstorming threats.
It represents:
Spoofing, Tampering, Repudiation, Information Disclosure, Denial of Service, and Elevation of Privilege.
You do not need to mechanically apply every category to every class.
Instead, use STRIDE to challenge assumptions.
For an authentication flow, ask whether someone could impersonate another user.
For locally stored information, ask whether it could be modified or disclosed.
For a privileged backend operation, ask whether a normal account could gain elevated authority.
Consider a payment request.
A threat model might explore whether an attacker could alter the amount, replay a previous request, substitute another account ID, steal the authentication token, or bypass local confirmation.
Notice that these questions describe business failures rather than Android implementation details.
That is what makes threat modeling useful.
The framework guides thinking, while the application context determines what actually matters.
Model Abuse Cases, Not Only Technical Vulnerabilities
Traditional testing often asks:
“Does the feature work?”
Threat modeling asks:
“How could someone intentionally use this feature incorrectly?”
Imagine a referral system that rewards users when friends register.
The implementation may be technically secure. HTTPS works, authentication works, and the database has no obvious injection issue.
But what happens if one user automates thousands of fake registrations?
That is an abuse case.
Other examples include repeatedly claiming promotions, manipulating order sequences, sharing premium accounts, scraping valuable content, or abusing password-reset workflows.
Modern mobile security therefore needs to consider business logic alongside technical vulnerabilities.
OWASP MASVS covers major areas such as storage, cryptography, authentication, networking, platform interaction, code security, resilience, and privacy, but OWASP also notes that MASVS should be used alongside secure architecture and threat modeling.
A checklist can tell you whether encryption exists.
A threat model asks whether encryption solves the actual problem.
Examine Android-Specific Entry Points
Android creates several platform-specific boundaries worth reviewing individually.
1. Exported Components
An exported Activity or Service may be invoked by another application.
Check whether the caller needs authorization and whether incoming Intents are validated.
Android security guidance recommends safer inter-app communication practices and limiting unnecessary exposure.
2. Deep Links
Never assume parameters are trustworthy simply because the URI looks familiar.
Authorization decisions should come from authenticated application or backend state rather than route parameters.
3. WebView
Ask which URLs can load, whether JavaScript is necessary, and whether native interfaces are exposed.
Remote web content combined with powerful native bridges can create dangerous trust relationships.
4. Local Storage
Identify which data really needs to remain on the device.
OWASP’s mobile security model specifically treats data-at-rest protection as its own security area.
Every additional entry point deserves one simple question:
Who controls the input?
The answer often determines how defensive the receiving code should be.
Do Not Forget Third-Party SDKs and Dependencies
Your threat model should include code your team did not write.
Analytics tools, advertising SDKs, authentication libraries, payment components, networking packages, and build dependencies all become part of the final application.
A compromised dependency can introduce behavior that bypasses your own architectural assumptions.
OWASP explicitly identifies compromised libraries, SDKs, and build tools as possible supply-chain paths for malicious code entering a mobile application.
Ask what each dependency can access.
Does an analytics SDK receive user identifiers?
Can an advertising SDK access location?
Does a third-party library process authentication data?
Is the library still maintained?
Dependency reviews should therefore consider both vulnerabilities and privileges.
A perfectly implemented feature can still leak information if a dependency receives more data than it actually needs.
Rank Risks Instead of Treating Everything Equally
A threat model that produces 200 “critical” threats is not useful.
Prioritization matters.
A simple approach is to consider:
Likelihood × Impact
A theoretical attack requiring physical possession, root access, specialized hardware, and several hours of work may rank differently from an authorization flaw exploitable remotely by any normal user.
Impact matters too.
Compromising a cached profile picture is different from transferring money from another account.
The purpose of ranking is not mathematical perfection.
It is helping teams decide where engineering effort produces the greatest reduction in risk.
High-impact, easy-to-exploit threats should naturally move toward the top.
Lower-risk problems may still deserve fixes, but they should not displace controls protecting critical assets.
This prevents threat modeling from becoming an endless documentation excercise.
Connect Threats to Concrete Controls
Every meaningful threat should lead to a security decision.
Suppose the threat is:
A malicious app launches an internal transaction Activity.
Possible controls may include making the Activity non-exported, requiring an application permission, validating caller identity, or moving critical authorization to the backend.
If the threat is:
An attacker modifies a client-side subscription flag.
The primary control should probably be server-side entitlement verification rather than another complicated local Boolean.
If the threat involves a tampered application environment, Play Integrity may provide an additional risk signal. Android recommends using app-integrity information to help backend systems identify potentially modified applications and risky interactions.
The mitigation should match the threat.
Adding encryption to a deep-link authorization bug will not fix the authorization problem.
Good threat modeling keeps security controls connected to specific failure scenarios.
Update the Threat Model as the Product Changes
Threat modeling should not be a one-time meeting before version 1.0.
Applications evolve constantly.
A team adds WebView-based checkout.
A new analytics SDK appears.
The backend introduces file uploads.
Deep linking is expanded.
A new premium subscription feature changes what attackers can gain.
Each change can alter the threat landscape.
OWASP recommends revisiting security requirements when new features and data classes are introduced, particularly in iterative development environments.
Make threat modeling part of normal architecture review.
It does not need to become a massive meeting every sprint.
For a new feature, developers may only need to ask:
What valuable assets are introduced?
What new data enters?
Where does trust change?
What can an attacker control?
What happens if our assumptions fail?
That lightweight habit can prevent expensive security redesigns later.
Advanced threat modeling for modern Android applications is less about predicting every possible hacker technique and more about understanding where the application places trust.
Start with valuable assets, map data flows and trust boundaries, identify Android-specific attack surfaces, define realistic attacker capabilities, and explore abuse cases alongside technical vulnerabilities.
Then rank threats according to likelihood and impact before connecting the highest risks to concrete controls.
Most importantly, keep the model alive as the product evolves.
Take one sensitive workflow in your own Android app – login, payment, account recovery, file sharing, or subscription access – and draw its complete data flow.
Mark every place where information crosses a trust boundary. Those boundaries are usually the best places to start your next security review.