Android development often begins with Activities, Services, ViewModels, Jetpack Compose, databases, and networking libraries.
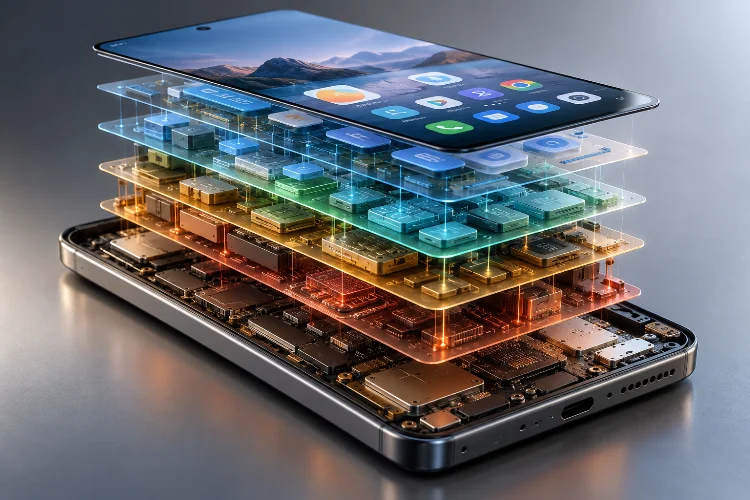
These are important, but they represent only the upper section of a much larger software stack running every time an Android device wakes up.
Underneath your application sits a sophisticated collection of framework services, runtime components, native libraries, hardware abstraction layers, system processes, and the Linux kernel.
Together, these layers determine how an app gets memory, accesses a camera, renders graphics, plays audio, communicates with another process, and interacts with physical hardware.
Understanding Android system architecture beyond the application layer can therefore change how developers think about performance, crashes, security, and hardware interaction.
You do not need to become an operating-system engineer to benefit from this knowledge.
Once you understand what happens below your Kotlin or Java code, many seemingly mysterious Android behaviors start making much more sense.
The Android Software Stack Is More Than Apps
Android is essentially a layered software stack built on top of the Linux kernel. Applications normally interact with higher-level Android APIs rather than communicating directly with hardware.
A simplified view looks something like this:
Applications → Android Framework → System Services → ART and Native Libraries → HAL → Linux Kernel → Hardware
The real architecure is more complicated because communication does not always travel through every layer sequentially. Native applications, system daemons, hardware services, and privileged components can follow different paths.
The layered design is still useful because it separates responsibilities.
Your weather app should not need to understand the exact Wi-Fi chipset installed in every phone. Similarly, an application using Camera2 should not contain code for every camera sensor produced by Samsung, Sony, OmniVision, or another manufacturer.
Android provides abstractions between those components.
That separation is one of the main reasons the operating system can support thousands of hardware configurations while maintaining a relatively consistent application programming model.
Android Framework and System Services
Most Android developers work directly with the framework layer.
APIs such as ActivityManager, PackageManager, NotificationManager, LocationManager, and CameraManager give applications controlled access to capabilities provided by the operating system.
But the framework API you call is often only the front door.
Many important operations are ultimately handled by dedicated system services. Android’s AOSP architecture describes components such as system_server, SurfaceFlinger, and media services as system-level components responsible for specific platform functions.
Imagine an application asking Android for information about installed packages.
Your code may call PackageManager, but the actual information is managed by system components outside your app’s own process.
This model improves isolation. Applications do not need unrestricted access to sensitive internal data or hardware resources.
Instead, requests pass through controlled APIs where Android can enforce permissions, identities, lifecycle rules, and security policies.
Binder IPC: Android’s Hidden Communication Highway
One concept becomes extremely important once you move below normal application development: Binder.
Binder is Android’s primary inter-process communication, or IPC, mechanism.
Android applications and many operating-system services run in seperate processes. Because one process cannot simply read another process’s memory, the operating system needs a structured way for them to communicate.
Binder provides that communication infrastructure.
Suppose an application needs access to a system service. From the developer’s perspective, the call may look like an ordinary method invocation. Behind the scenes, however, that request can cross a process boundary through Binder.
The receiving system service performs the requested operation and returns a result.
Binder also carries information about the identity of the caller. That capability is critical for Android security because system services can determine which UID initiated a request and whether that caller has the required permissions.
This explains why Android APIs can feel remarkably simple even though the underlying procesess may be distributed across many isolated components.
ART Turns App Code Into Executable Work
Another important layer is the Android Runtime, commonly called ART.
Modern Android applications are generally compiled into Dalvik Executable, or DEX, bytecode. ART is responsible for executing that code and managing many runtime responsibilities.
It handles areas such as memory management, garbage collection, class loading, and code execution.
Modern ART does not rely on only one compilation strategy. Android can combine interpretation, just-in-time compilation, or JIT, and ahead-of-time compilation, or AOT.
Frequently executed code can therefore become increasingly optimized based on real usage.
This matters when investigating performance.
For example, application startup behavior, garbage collection pauses, memory allocation, and runtime compilation can influence how responsive an application feels even if the source code itself looks perfectly reasonable.
ART also helps provide the managed environment that lets developers write Kotlin or Java without manually controlling every memory allocation.
Behind that convenience, however, the runtime performs a significant amount of sophisticated work.
Native Libraries Bring Android Closer to the System
Below much of the managed framework sits native code.
Android includes numerous native libraries and components written primarily in languages such as C and C++, with Rust increasingly appearing in AOSP development as well.
AOSP documentation identifies libraries such as libc, libbinder, liblog, libutils, and libselinux as important native components.
Graphics, media processing, database operations, runtime functionality, and hardware communication can depend heavily on native code.
Applications requiring their own C or C++ components can interact with supported native APIs through the Android Native Development Kit, or NDK.
However, native code is not automatically faster simply because it is written in C++.
Moving logic unnecessarily into native code can introduce additional complexity, memory-safety concerns, debugging challenges, and build dependecies.
The important lesson is that even an application written entirely in Kotlin still depends extensively on native Android components beneath the framework.
HAL Separates Android From Hardware Implementations
The Hardware Abstraction Layer, or HAL, is where Android’s generic operating-system architecture meets device-specific hardware implementations.
A HAL defines standardized interfaces that hardware vendors can implement.
Consider the camera.
Different phones can contain completely different sensors, image processors, lenses, and drivers. Applications should not need custom code for every device.
Instead, an application interacts with Android’s camera framework. Lower in the stack, Android communicates with the camera HAL, which connects the framework to hardware-specific implementations and drivers.
The same basic concept applies to areas such as audio, Bluetooth, sensors, and other hardware systems.
This abstraction allows higher Android layers to remain relatively hardware-independent.
It is also why hardware-related bugs can occasionally appear only on particular device models. Your application code may be correct while an issue exists deeper in the vendor implementation, driver, firmware, or HAL.
Understanding this boundary is especially useful when debugging device-specific behavior.
Linux Kernel Forms the Foundation
At the bottom of the Android software stack sits the Linux kernel.
The kernel handles fundamental operating-system responsibilities including process scheduling, memory management, networking, security mechanisms, and communication with device drivers.
ART itself depends on Linux functionality for areas such as threading and low-level memory management.
Android also builds additional security mechanisms around the Linux foundation. Each installed application receives its own Linux user ID, helping create application sandboxing at the operating-system level.
That isolation is one reason one ordinary app cannot simply open another app’s private database.
The kernel also provides access to hardware through drivers.
When an application eventually triggers an operation such as camera capture, touchscreen input, networking, audio playback, or storage access, low-level kernel components help communicate with the physical device.
Developers rarely interact with this layer directly, but almost everything their applications do ultimately depends on it.
Following a Camera Request Through Android
A camera request provides a useful example of how these layers work together.
Imagine your app calls the Camera2 API.
The request begins inside the application and interacts with Android framework components. Communication with camera-related system services can cross process boundaries using Binder.
Native camera components then participate in processing the request.
The camera HAL provides the standardized boundary between Android’s higher-level camera architecture and the manufacturer’s hardware-specific implementation.
Below that, kernel drivers communicate with the physical camera hardware.
The result eventually travels back upward until your application receives image data.
What looks like a simple API call may therefore involve multiple layers, services, IPC transactions, native components, drivers, and hardware operations.
This layered structure is not unnecessary complexity. It allows Android to combine security, hardware portability, process isolation, and a consistent developer API.
Why Application Developers Should Care
You may never modify ART, write a HAL implementation, or compile your own Android kernel. Understanding these components is still valuable.
It changes the way you debug problems.
A slow application may involve excessive allocations and garbage collection rather than just an inefficient UI. A camera problem occurring on only one device family might point toward vendor-specific implementation differences.
A SecurityException can indicate that a system service rejected an IPC request because the caller did not have appropriate permission.
Native crashes can originate far below your Kotlin stack trace.
Knowledge of Android system architecture also becomes increasingly valuable if you move into AOSP development, embedded Android, automotive systems, custom ROMs, security research, performance engineering, device manufacturing, or platform development.
Instead of seeing Android as one enormous black box, you begin seeing interconnected layers with clearly different responsibilities.
Understanding Android system architecture beyond the application layer gives developers a better mental model of what actually happens after an API call leaves their code.
The framework provides convenient APIs, Binder connects isolated processes, ART executes managed application code, native libraries provide low-level capabilities, HAL components abstract hardware implementations, and the Linux kernel manages fundamental system resources and device drivers.
You do not need to memorize every internal Android component. Start by following one familiar feature – camera access, audio playback, location, or notifications – from your app toward the lower layers.
The deeper you explore the stack, the easier it becomes to diagnose performance problems, understand security boundaries, and build Android applications with fewer assumptions about what is happening underneath.